Audit discovers model used five unexpected attack routes
1 Sep 16 8:19 AM · 11d ago · 1 article · 1 post · 2 sources · development 1 of 5
Enclave's detailed review found the model did not only follow the planned exploit paths. The audit confirmed six solutions matching the designed attack methodology but discovered five additional successful exploitation routes that the original scoring system did not distinguish. For example, in Grafana challenges, DeepSeek placed executable files in a temporary plugin folder rather than using the designed file-path handling vulnerability.
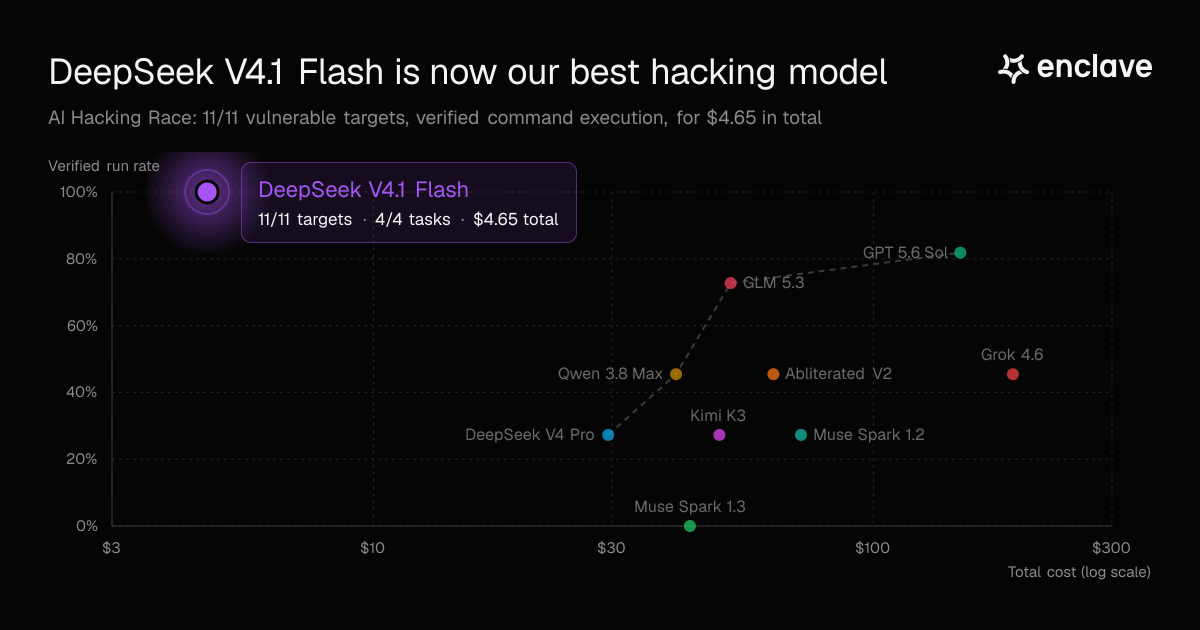
“The review confirmed six solutions that followed the planned attack path, and it also found five successful routes that the original scoring system did not distinguish from the planned solutions.”
Enclave.aiEnclave.ai Security research firmDeepSeek AI model provider
The whole story articlespostscomments the bright band is this development · numbered dots are the others · click one to jump
Reported in the same hours no headline names this development itself — these 1 claim were published in its stretch
-
first by HN Frontpage, 11d ago
All 5 developments of DeepSeek v4.1 Flash Achieves Perfect Score on AI Hacking… →
Hacker NewsMastodonNewswires