Lobsters community discussion surfaces implementation concerns
2 Sep 21 1:53 PM · 2d ago · 2 posts · 11 comments · 2 sources · development 2 of 2
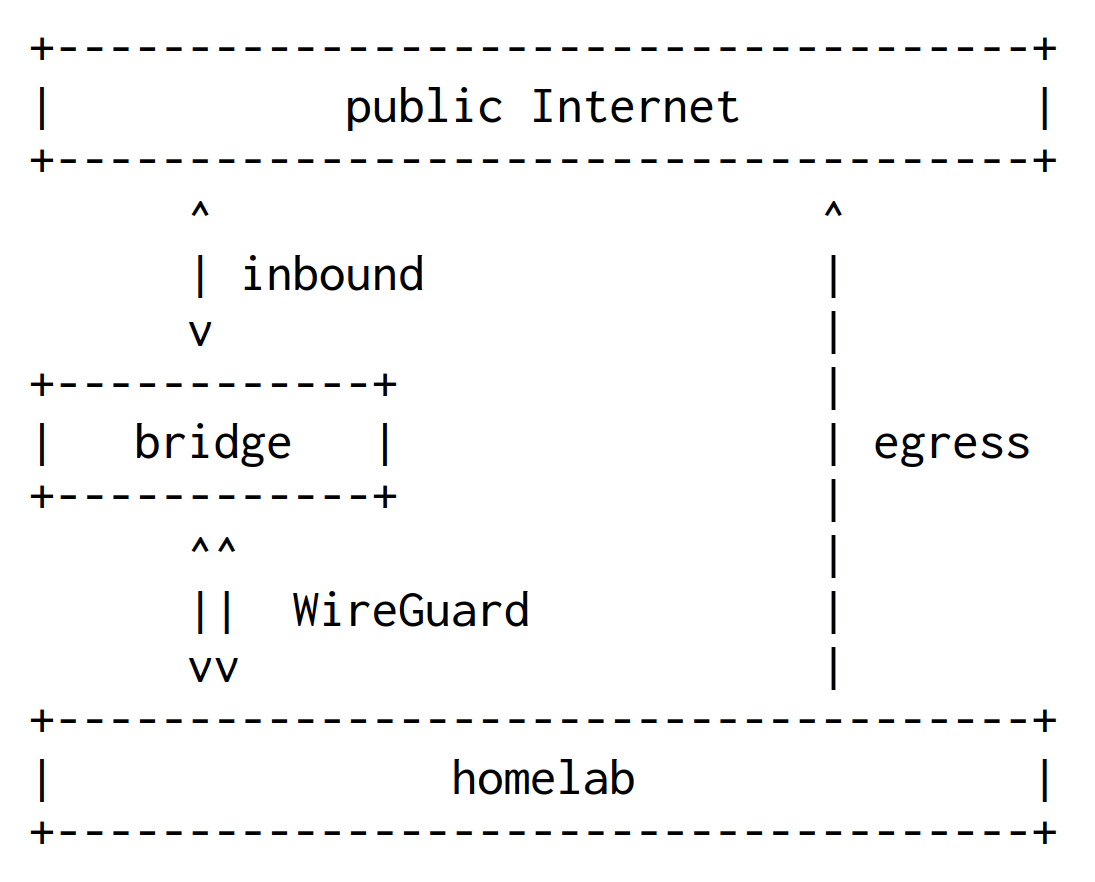
The post reached Lobsters where developers engaged with the technical approach, raising questions about security, cost trade-offs, and alternative solutions. Commenters discussed whether using a VPS for the bridge made sense versus running services directly on the VPS, and surfaced security concerns about full network connections between bridge and home.
“If I have to pay for a VPS anyway, why not run my services on it?”
singpolyma, Lobsters commenter · lobsters ↗David Alvarez Rosa Author, software engineer
The whole story postscomments the bright band is this development · numbered dots are the others · click one to jump
What people said 24 voices · best of 43 · verbatim
-
You can pay for a very cheap VPS as a proxy and then run more expensive compute and storage locally.
-
If I have to pay for a VPS anyway, why not run my services on it?
-
> But I don't really feel comfortable with a full connection between a bridge and home network. I suppose this isn't that different from exposing a server in your physical network to the internet. But it still does give people potential access to your entire network when something on the bridge is configured wrongly. You can practice defense in…
-
I asked myself that question years ago...and then i went to self-host Nextcloud on a VPS and realized that my storage needs outgrew what was reasonably cost-effective VPS storage...so then i moved my nextcloud instance to my homelab, etc. So, while i agree you with you that sometimes keeping stuff up on a VPS makes sense, and other times/use-cases…
-
You can set the [CAA record](https://letsencrypt.org/docs/caa/) to restrict accepted challenge types to the dns challenge, which should mitigate this.
-
If you are planning to selfhost for next 10+ years, buying the hardware will always be cheaper than cloud
-
Interestingly this is something I have been thinking about as well. But I don't really feel comfortable with a full connection between a bridge and home network. I suppose this isn't that different from exposing a server in your physical network to the internet. But it still does give people potential access to your entire network when something…
-
I've got a similar thing going with an Oracle free forever VPS. Too scared to wean myself off of Tailscale right now though :(
-
Good that I have IPv6 both on my phone and home Internet connection, I don't have to do all those hacks anymore
-
If your goal is "not relying on abusive cloud corporations" it's worth keeping in mind that (for many deployments/purposes) the VPS is in a crucial trusted position. Even if you push the TLS down to your home server, anyone who gets access to your VPS, such as a hacker or employee of the provider, has the ability to request a new LE cert and start…
-
It's true, though I learnt recently that [at least one well-known provider] is offering "older" dedicated servers with lots of disk at a heavy discount. For me it's a sweet spot vs dealing with a server in the house.
-
I run the same setup at home currently with a VPS at the local hackerspace. A similar post was written by mjg about the same thing.
-
Unrelated but I love the [initial](https://en.wikipedia.org/wiki/Initial) at the start of the article
-
As an individual, you really can’t. The web is built on a lot of institutional trust and you can only get so far without it. I say this not as some kind of “gotcha” - it’s honestly really hard to homestead services on the open internet without leaning on others you’d probably rather not. So for self-hosting it’s worth asking whether some decision…
-
Those are good actions to take, but also increase the sysadministrative overhead I have to manage. I personally don't find it fun to do sysadmin work for what I consider my personal "production" environment as I just want it to work. Which is why for my use case I went with the simpler autossh portforwarding solution where I can build in a lot of…
-
I like to put this as: Calculate your expected annual spend on the VPS capable of hosting what you want comfortably, then check what you can get in eBay for that one-off price. Usually it will be a massive upgrade. Factor in the electricity cost though, and ensure at least two mirrored drives.
-
Even if it's not the practical thing to do and you might be forced to proxy through a VPS, it's _nice_ (for some) to self-host, and get experience with running services on bare metal. After all, self-hosting in general is rarely done for purely practical purposes.
-
Thanks! I picked from the LaTeX catalogue for drop caps
-
Many people talk about using Wireguard® to connect a public IP on a VPS to machines elsewhere (usually at home). I've always wondered how you do this without NAT, but nobody has given any real world examples. This article finally has a real world example, showing how it's done with NAT (which we all have to assume is necessary, unless IPs are…
-
With VMs arp doesn't really matter. Your provider on the remote side sends traffic to the VM explicitly and there's no L2 discovery happening at all. On your side you add a dummy interface for the IP so it doesn't send any announcements on real media either. The tunnel like wg gets the traffic because of its configuration and also doesn't care…
-
If you have two public IPs on the VPS, you could route one to your without a NAT. With a single IP... you could probably do something like that, but the management traffic would get slightly tricky - you'd need to ensure the SSH / tunnel traffic doesn't loop into the tunnel too.
-
I wrote about something similar [earlier](https://yashgarg.dev/posts/reverse-proxy-cgnat/), for which I use Tailscale. I use it pretty extensively across [my setup](
-
Usually you also need to adjust MTU lower for this to work
-
I appreciate the response, but unfortunately you're writing the same thing that many other people have said, without a specific example. Nobody has yet explained how to "route", if that's even the correct term here, that second IP if the upstream router doesn't know to send that traffic anywhere but to the same segment as the VPS. I've used…
All 2 developments of Developer publishes guide to self-hosting behind CGNAT… →
Hacker NewsLobsters