SecurityQuiet 79d · day 82
9,300+ exposed AWS keys still active, hundreds give full admin control
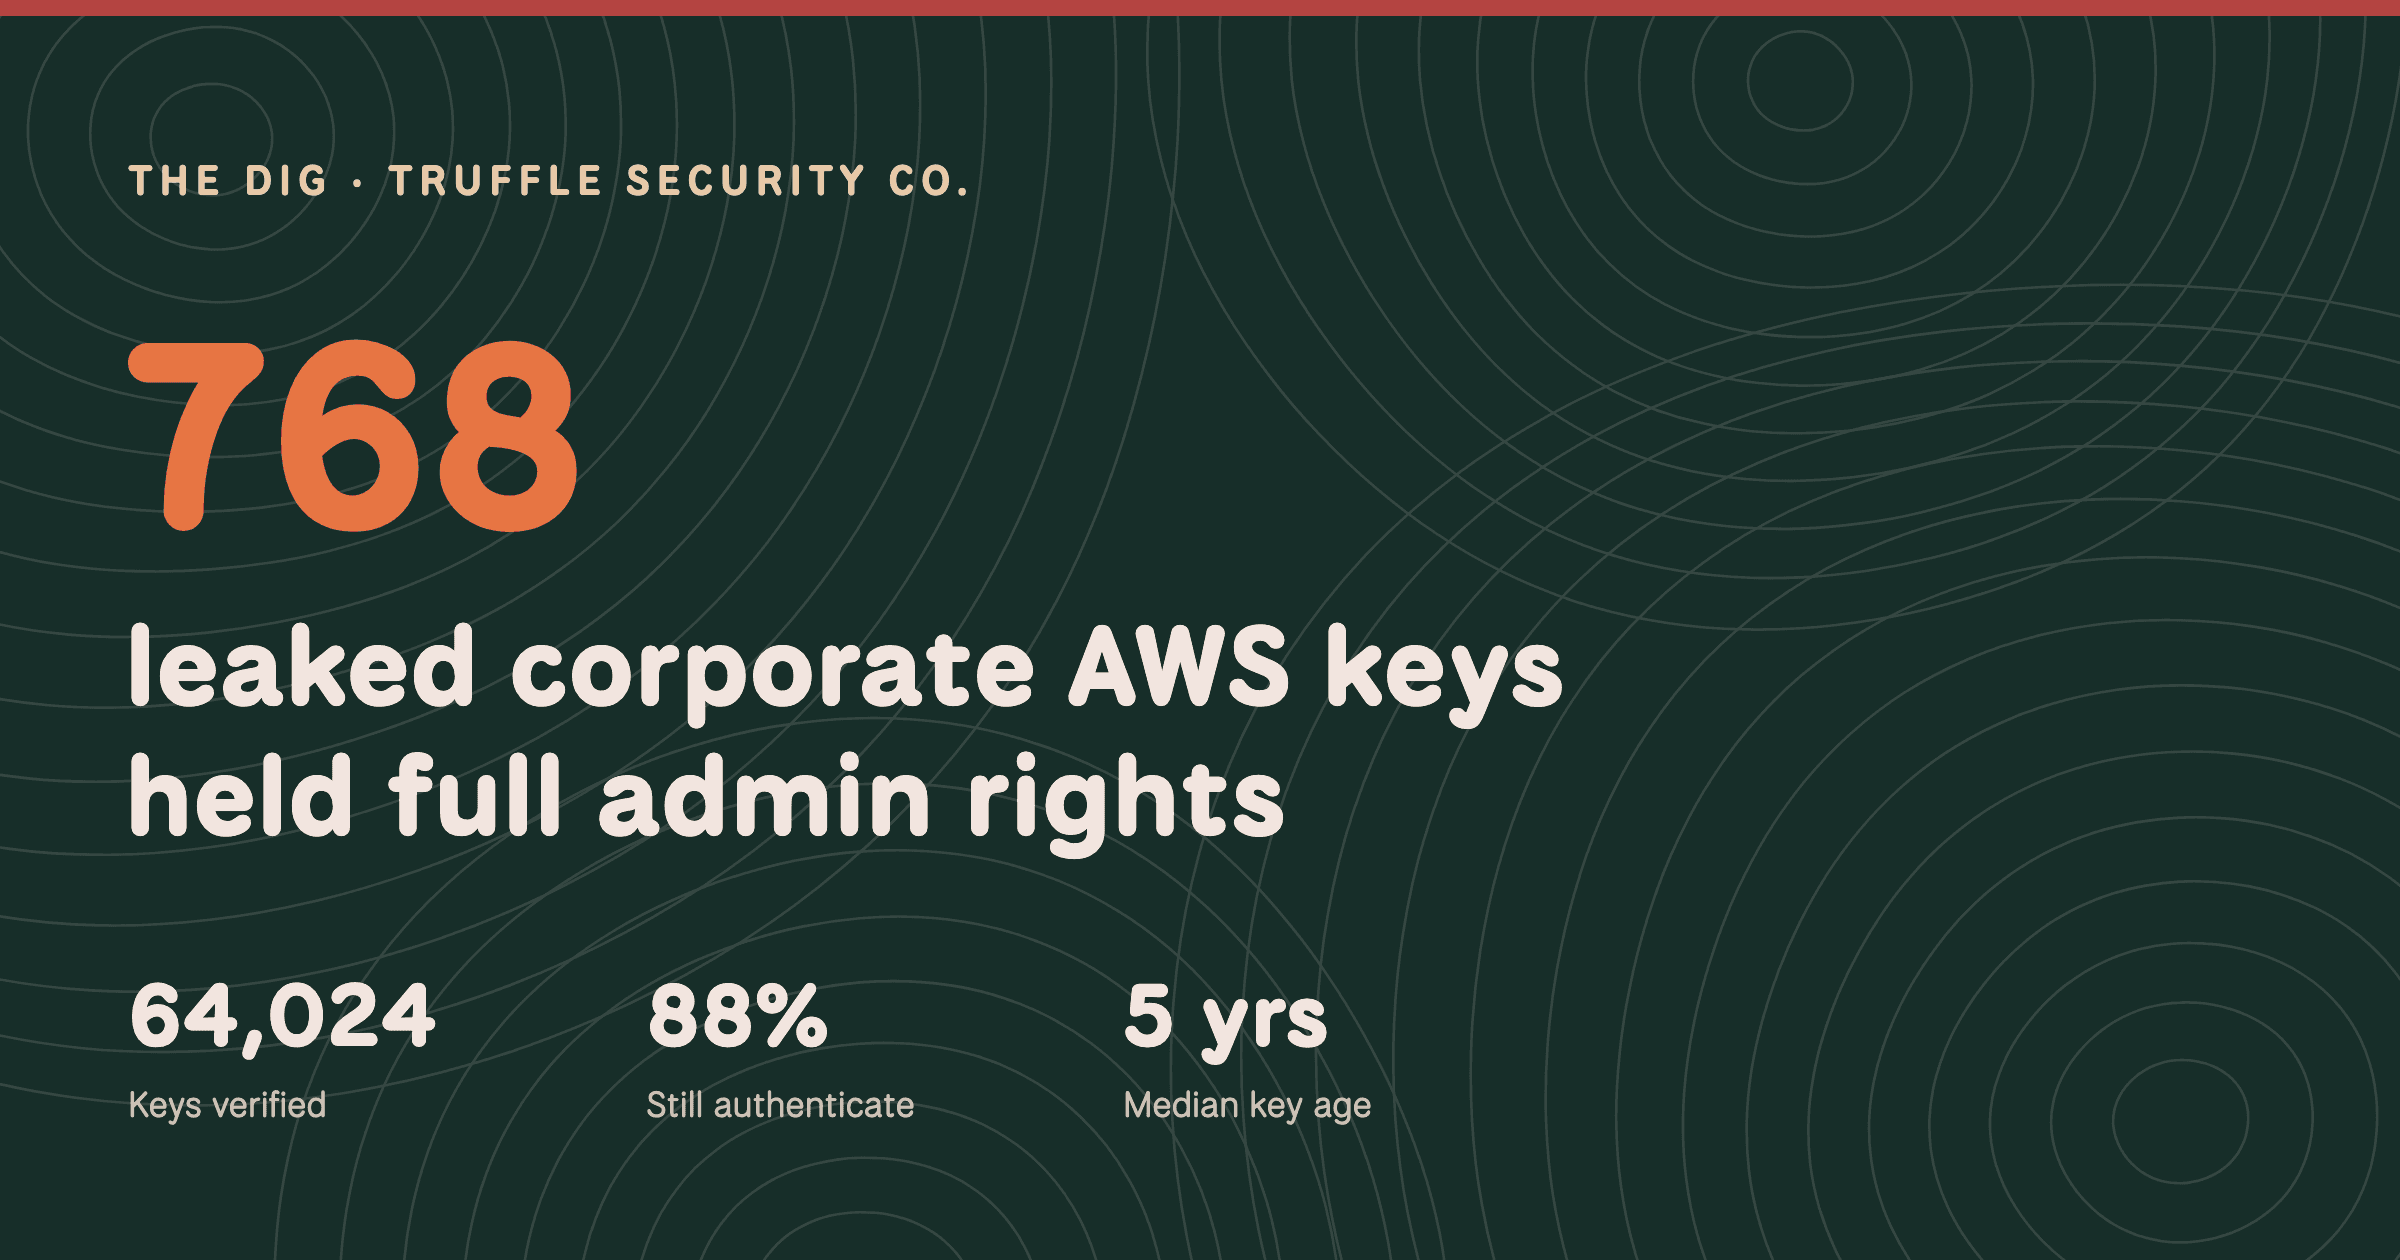
Truffle Security's four-year scan finds thousands of live AWS credentials in public repos, with 768 granting complete account takeover.
What to know
- Truffle Security found 9,300+ AWS access keys exposed since 2022 that remain active, with 768 giving full administrative control of corporate accounts.
- Only 262 of 2,754 readable accounts had budget alerts configured, leaving companies exposed to undetected cryptomining or data-wiping abuse.
- Most exposed keys had never been rotated — median age of about five years, with the oldest exposed for 17.4 years.
- Hugging Face was the single largest source of leaked keys (8,482), nearly 18% of which were root credentials with unrestricted access.
Truffle Security Security research firmAmazon Web Services (AWS) Cloud provider whose keys were exposedHugging Face AI model/dataset hosting platformBill Toulas BleepingComputer reporter
The record 2 articles and posts · last 30 days