Google Uses AI to Rewrite C Code to Rust, Targeting Memory Vulnerabilities
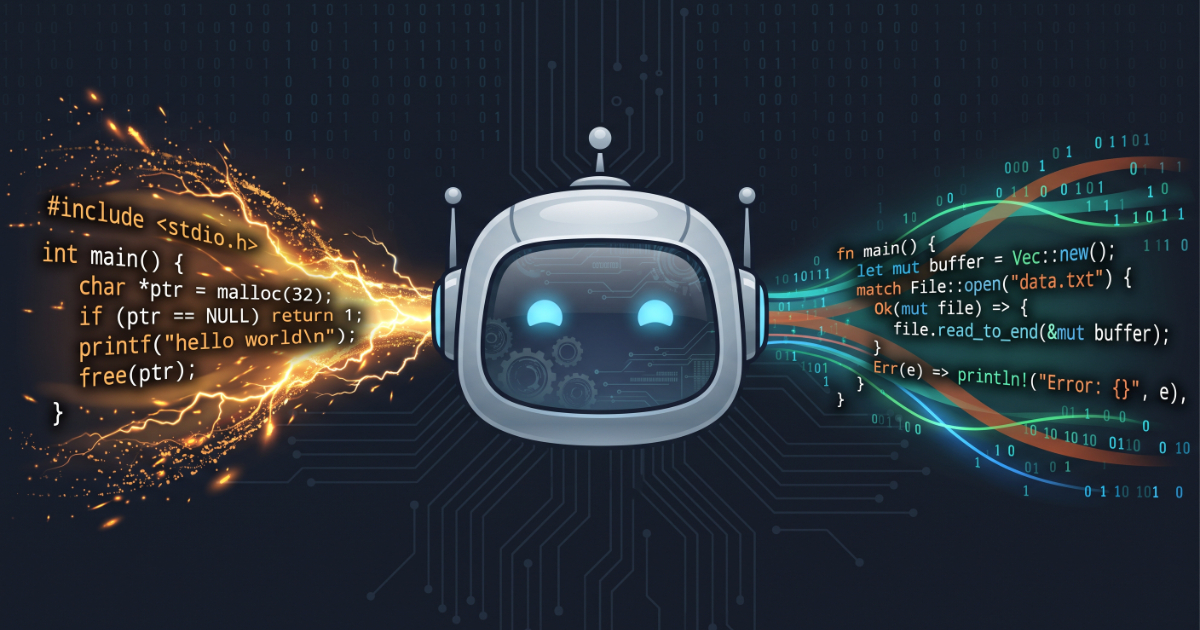
Google's security team deployed Gemini to translate legacy C dependencies into memory-safe Rust, starting with the giflib image library.
What to know
- Google deployed Gemini to automatically translate legacy C code into memory-safe Rust, starting with giflib (a 3,000-line image library handling untrusted input).
- The method paired AI translation with differential fuzzing to ensure compatibility and maintain runtime performance while eliminating memory vulnerabilities.
- Google found that AI-generated translations require ongoing human oversight, establishing a validation model for systematic legacy-code replacement.
- This approach offers a scalable pathway for addressing memory vulnerabilities across critical infrastructure dependencies.
“Google's security team developed a method to replace legacy C code in the giflib image-processing library with Rust, targeting inherent memory vulnerabilities.”
InfoQ · InfoQ ↗ · Sep 26
Google Security Team Project initiator and executorGemini AI translation engine
How it unfolded 1 development · click the chart to see its coverage articlesposts
-
background
Google publishes details on AI-assisted rewrites with differential fuzzing — Google announced the completed project, detailing how they used AI translations alongside differential fuzzing to ensure compatibility and maintain runtime performance while mitigating zero-day vulnerability risks.
-
1
Google security team develops AI-assisted C-to-Rust translation method
Google's security team validated a method to eliminate legacy memory vulnerabilities by leveraging Gemini to translate C codebases into memory-safe Rust equivalents. The initiative focused on giflib, an image-processing library with about 3,000 lines of code that often decodes untrusted data.
Also covered reported alongside — the timeline has no entry for these yet
-
first by infoq.com, 1d ago · also InfoQ