Polymarket hit by wallet-draining malware in third-party script
Security researchers found code in a performance monitoring tool that stole user credentials and assets; $2M in holdings detected at attacker address.
What to know
- A malicious JavaScript file served through Polymarket's DebugBear integration could access user trading sessions, inspect portfolios, and transfer assets.
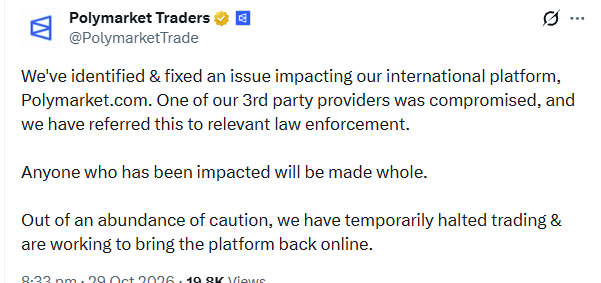
- Polymarket removed the compromised integration from production build on October 29, the same day Hudson Rock confirmed the threat.
- Over $2 million in holdings detected at the attacker's hardcoded address, though verified total losses and affected user count remain unknown.
- The initial compromise mechanism and exact exposure window are still unresolved.
“This is evidence of substantial holdings at an address explicitly selected by the payload. It is not a verified accounting of the proceeds of this incident.”
Hudson Rock, Security researcher · InfoStealers ↗
Hudson Rock Security researcherPolymarket Affected platformVivian Community reporter
How it unfolded 1 development · click the chart to see its coverage articles
-
1
Wallet-draining code confirmed in performance monitoring tool
Hudson Rock analysis confirms the DebugBear script searched for logged-in users' trading clients, inspected portfolios, and attempted to sell or transfer assets. The script had a fallback recipient address containing over $2 million in holdings at the time of review.
“A performance-monitoring integration should measure how quickly a page loads. The JavaScript…does something far more consequential: it searches for a logged-in user's trading client, inspects their portfolio, and attempts to sell or transfer their assets.”
— Hudson Rock -
first by InfoStealers, 13d ago
-
-
background
Hudson Rock researchers retrieve malicious script from Polymarket integration — Security researchers downloaded JavaScript from cdn.debugbear[.]com/C7xcKKrjUnXK.js and confirmed it contained code designed to access trading sessions, inspect portfolios, and redirect assets. A second retrieval minutes later returned identical bytes.
-
background
Polymarket removes DebugBear script from production build — Polymarket's build metadata records the removal of the DebugBear integration with change message 'chore(polymarket): remove debugbear rum script (#15337)' timestamped 17:59:20 UTC. The removal indicates Polymarket had detected and responded to the compromise.
-
background
Researchers unable to confirm total losses or affected user count — While $2.19 million in holdings was detected at the attacker's hardcoded address, Hudson Rock states the exact exposure window, number of affected users, and aggregate verified losses remain unresolved. Initial compromise mechanism also unclear.